
-
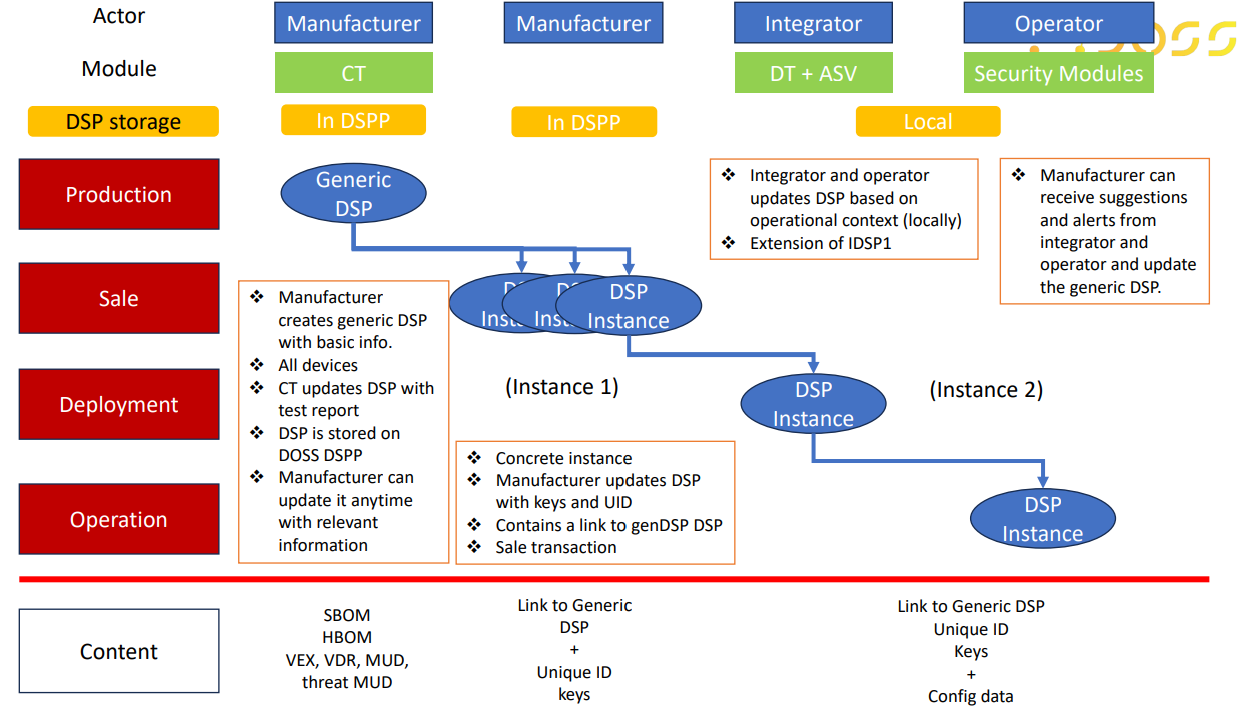
OSCAL as a foundation for a Device Security Passport: The DOSS project
With the rapid proliferation of IoT technologies, security concerns have increased due to the opaque nature of supply chains. Operators often lack comprehensive knowledge about the security status of their devices. The DOSS project addresses this gap by providing a system that facilitates transparency, reliability, and timely security information exchange among stakeholders of the IoT…
-
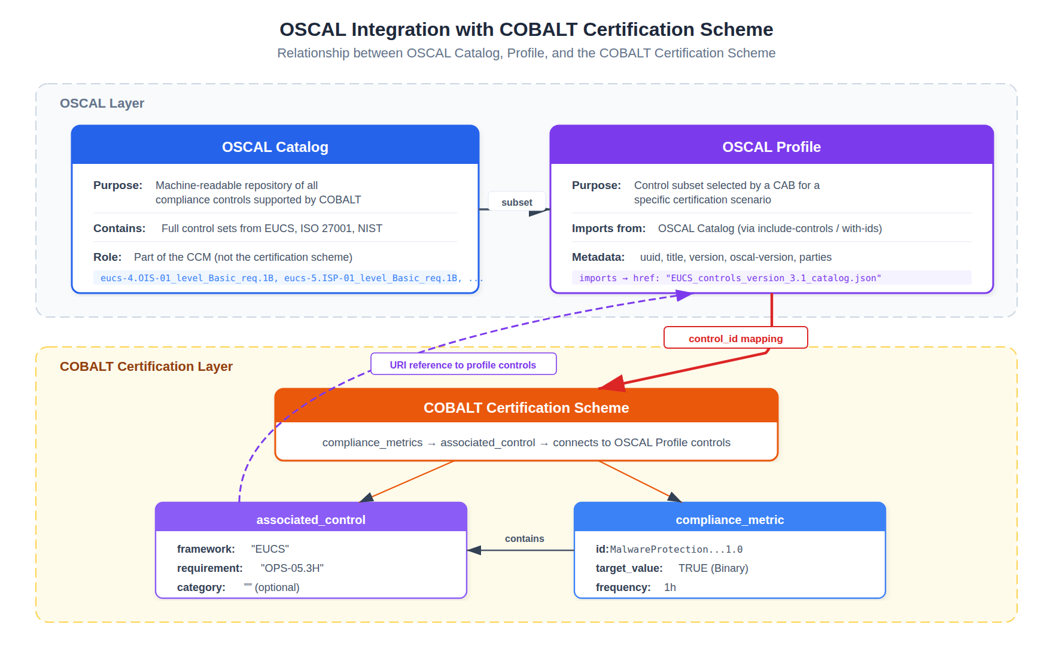
Using OSCAL for Continuous Cybersecurity Certification: The COBALT Experience
Demonstrating that a digital product or service is secure can involve navigating multiple standards, regulations and certification schemes. Overlapping requirements increase compliance costs, particularly for SMEs, while traditional audits provide only a snapshot of security that can become outdated as systems evolve. These challenges are increasingly relevant in the context of European cybersecurity legislation, including…
-
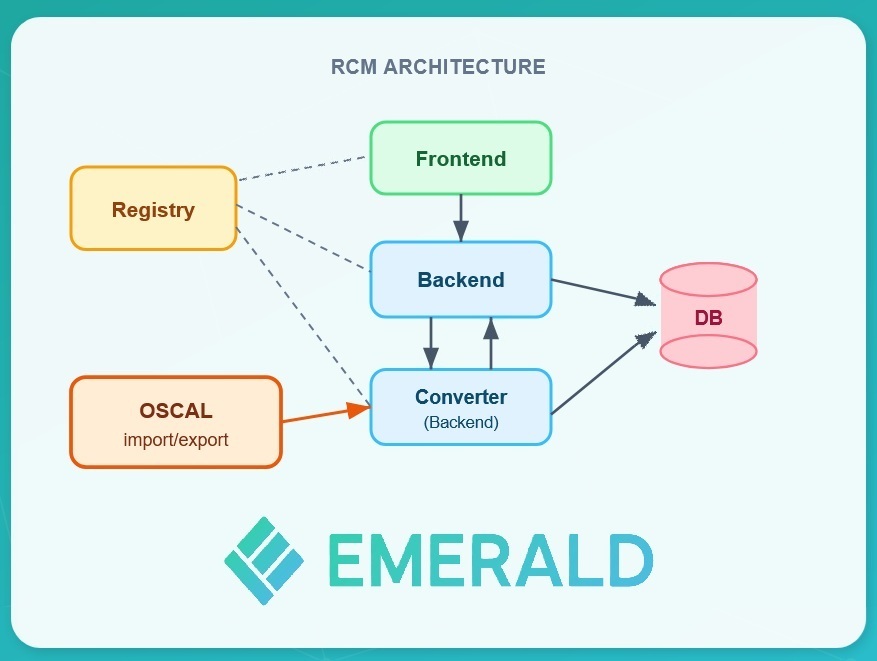
EMERALD: Building a Machine-Readable Future for European Certification with OSCAL
The EMERALD EU project has made significant progress in its work around OSCAL (Open Security Control Assessment Language), the open standard developed by NIST for expressing security compliance information in a machine-readable format. The project has developed and validated OSCAL templates for the EUCS, BSI C5, and AIC4 security schemes, and implemented import/export mechanisms in…
-

Kick-off of MEDINA’s EUROSCAL Initiative
During the i-4 Global Hybrid Forum 102 organized on June 26th 2023, our partner Bosch (represented by MEDINA’s technical manager Jesus Luna Garcia) will officially kick-off the EUROSCAL (EU Friends of OSCAL) initiative. This event has been carefully selected by the consortium because on one hand it gathers important members of the EU-based CISO community,…
Latest Posts
Please come back soon!