

EUROSCAL
The EU Friends of OSCAL
In order to promote the adoption of OSCAL in Europe, we are launching EUROSCAL (The EU Friends of OSCAL), as an open community of motivated individuals interested on leveraging OSCAL.
We seek to become a central EU hub for supporting the creation of synergies and sharing relevant information about OSCAL (including guidelines, reference implementations, and success stories).
Why OSCAL
Automation-based certification for Cloud Services in Europe
Since 2020 the EU-funded MEDINA project (952633) has been working on developing a framework for automating the cybersecurity certification of cloud services. Based on this experience, it has been identified that leveraging realistic levels of automation will be possible only if interoperability can be achieved. We refer in particular to the way cloud service providers communicate security requirements / catalogs, establish machine-readable baselines, maintain up-to-date descriptions of implemented controls, and automate their monitoring and assessment activities.
We, as EUROSCAL community, see OSCAL playing a critical role for supporting the achievement of these goals.

What is OSCAL
OSCAL framework
NIST, in collaboration with industry, is developing the Open Security Controls Assessment Language (OSCAL). OSCAL is a set of formats expressed in XML, JSON, and YAML. These formats provide machine-readable representations of control catalogs, control baselines, system security plans, and assessment plans and results.

NIST Open Security Controls Assessment Language
All official information related to OSCAL

Do not forget to visit NIST’s Open Security Controls Assessment Language pages for all official information related to OSCAL.
Furthermore, our colleagues from OSCAL.io maintain a community supporting OSCAL-enabled applicationse.
Who is who in EUROSCAL
EUROSCAL Resources
Please find below a collection of relevant EUROSCAL resources / activities within the European Union (EU). If you want to contribute with information about EU-resources not listed below, please contact us.

H2020 MEDINA Project
EU-funded R&D project developing a framework for automating the cybersecurity certification of cloud services. MEDINA is exploring OSCAL leverage for representing EU security catalogues, and security assessments.
HE COBALT Project
The COBALT project (Certification for Cybersecurity in EU ICT using Decentralized Digital Twinning) develops a model-driven framework for dynamic cybersecurity certification, building on and extending OSCAL model. By connecting structured certification information with operational evidence and risk assessment, COBALT explored how certification could become more automated, traceable and responsive to system changes.

ETSI TR 103 305-4
This ETSI Technical Report (Cyber Security (CYBER); Critical Security Controls for Effective Cyber Defence; Part 4: Facilitation Mechanisms), includes a presentation of OSCAL and how to serialize the “Critical Security Controls”.
HE DOSS Project
With the rapid proliferation of IoT technologies, security concerns have increased due to the opaque nature of supply chains. Operators often lack comprehensive knowledge about the security status of their devices. The DOSS (Design and Operation of Secure IoT Supply Chain) project addresses this gap by providing a system that facilitates transparency, reliability, and timely security information exchange among stakeholders of the IoT supply chain, including manufacturers, vendors, and integrators.
ETSI TR 103 305-4
This ETSI Technical Report (Cyber Security (CYBER); Critical Security Controls for Effective Cyber Defence; Part 4: Facilitation Mechanisms), includes a presentation of OSCAL and how to serialize the “Critical Security Controls”.
Collaborative paper on OSCAL
EMERALD and COBALT have collaborated in a research paper titled “Beyond Static Audits: Using OSCAL to Streamline Continuous Cybersecurity Certification“. This paper addresses the challenge of automating cybersecurity compliance and certification processes for cloud services and presents how OSCAL enables interoperable, machine-readable representations of security controls, implementations, and assessment results.
HE EMERALD Project
EU-funded R&D project EMERALD (Evidence Management for Continuous Certification as a Service in the Cloud) develops a framework to support Service Providers, Customers and Auditors in the certification process, fostering the adoption of cloud services and ensuring they are accessible, secure, and beneficial for all stakeholders involved. EMERALD is actively integrating OSCAL to standardize and automate its cloud compliance processes, thereby fostering seamless interoperability and continuous certification.
Blog
Latest Posts
-
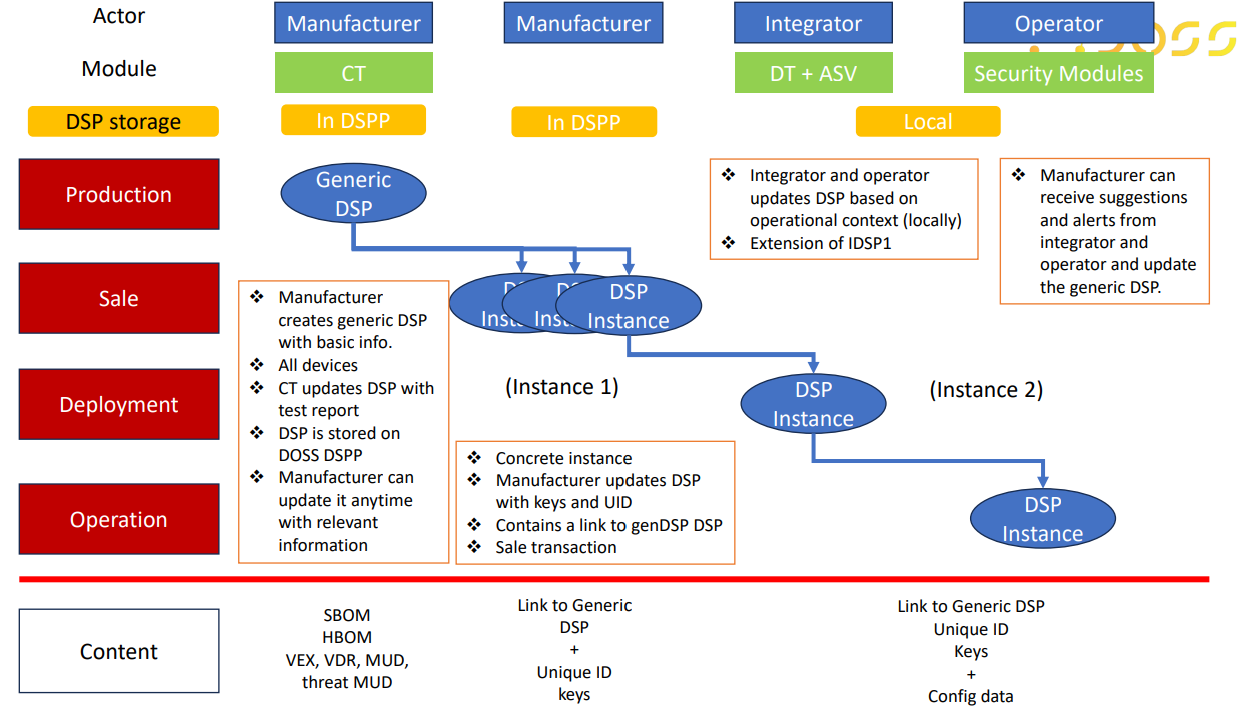
OSCAL as a foundation for a Device Security Passport: The DOSS project
With the rapid proliferation of IoT technologies, security concerns have increased due to the opaque nature of supply chains. Operators often lack comprehensive knowledge about the security status of their devices. The DOSS project addresses this gap by providing a system that facilitates transparency, reliability, and timely security information exchange among stakeholders of the IoT…
-
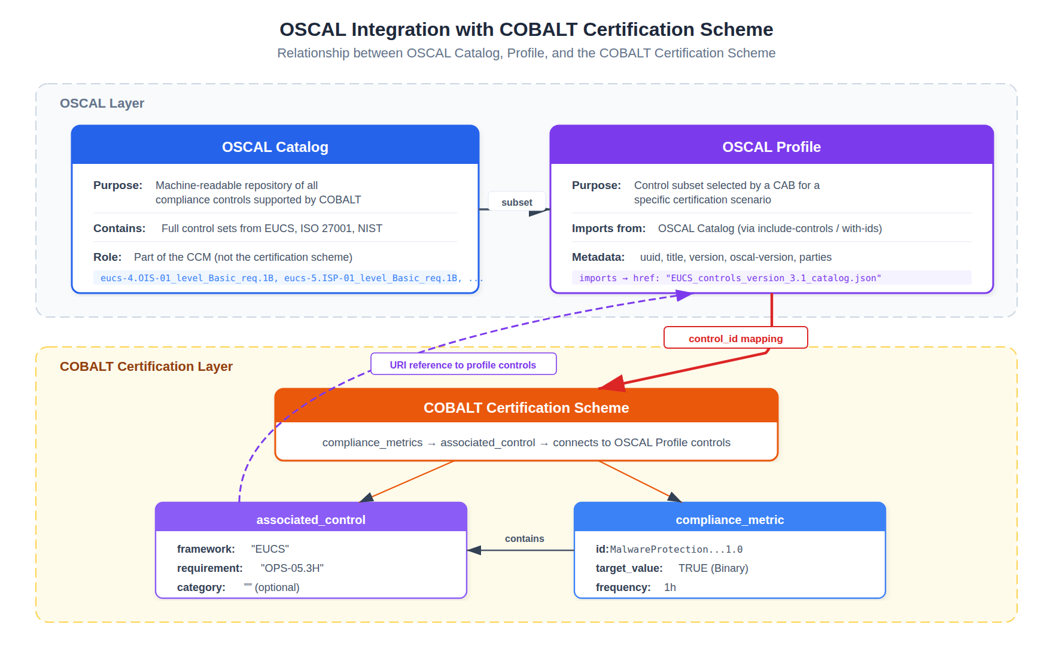
Using OSCAL for Continuous Cybersecurity Certification: The COBALT Experience
Demonstrating that a digital product or service is secure can involve navigating multiple standards, regulations and certification schemes. Overlapping requirements increase compliance costs, particularly for SMEs, while traditional audits provide only a snapshot of security that can become outdated as systems evolve. These challenges are increasingly relevant in the context of European cybersecurity legislation, including…
-
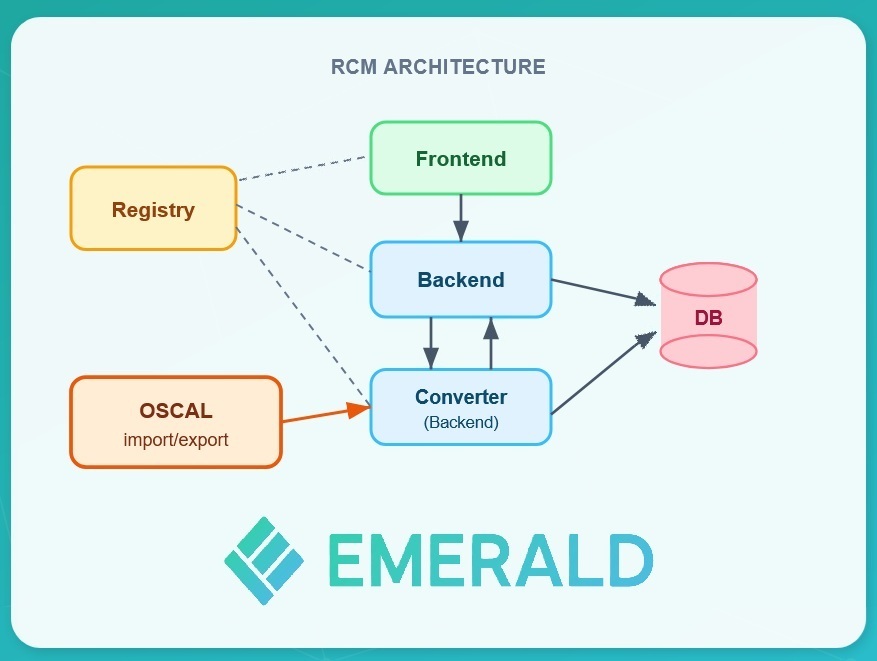
EMERALD: Building a Machine-Readable Future for European Certification with OSCAL
The EMERALD EU project has made significant progress in its work around OSCAL (Open Security Control Assessment Language), the open standard developed by NIST for expressing security compliance information in a machine-readable format. The project has developed and validated OSCAL templates for the EUCS, BSI C5, and AIC4 security schemes, and implemented import/export mechanisms in…
Join the EUROSCAL community
If you are interested in becoming part of our EUROSCAL community, please do not hesitate in contacting us.
