

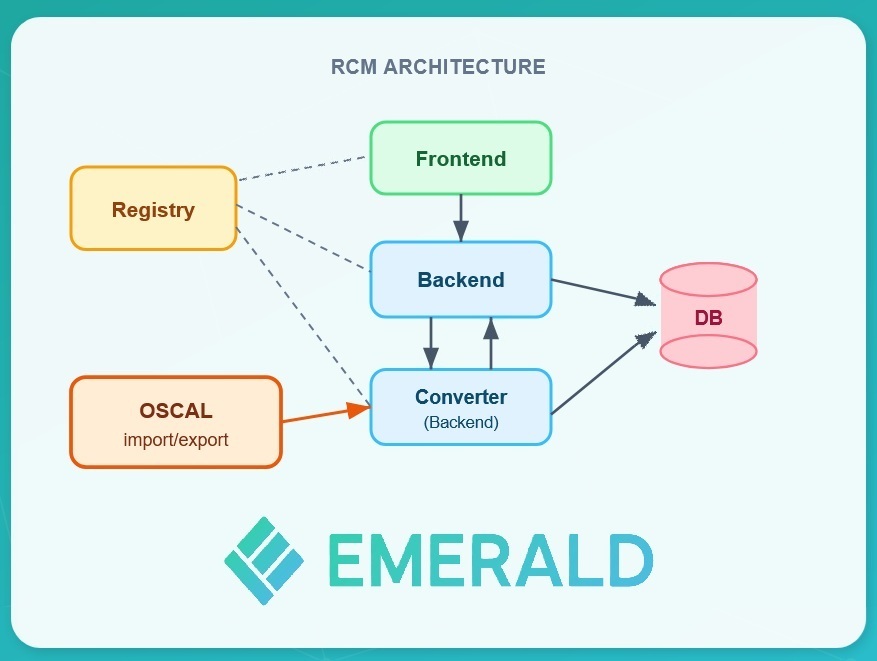
The EMERALD EU project has made significant progress in its work around OSCAL (Open Security Control Assessment Language), the open standard developed by NIST for expressing security compliance information in a machine-readable format. The project has developed and validated OSCAL templates for the EUCS, BSI C5, and AIC4 security schemes, and implemented import/export mechanisms in the Repository of Controls and Metrics (RCM) component that allow OSCAL-formatted schemes to be imported using these templates and, conversely, RCM schemes to be exported into the defined OSCAL format. In a notable simplification of the architecture, the original set of scheme-specific templates has been replaced by a single, universal template capable of exporting any scheme stored in the RCM to OSCAL. This change also ensures that the exported EMERALD catalogues open correctly in the OSCAL Catalog Viewer, improving interoperability and ease of use for the community.
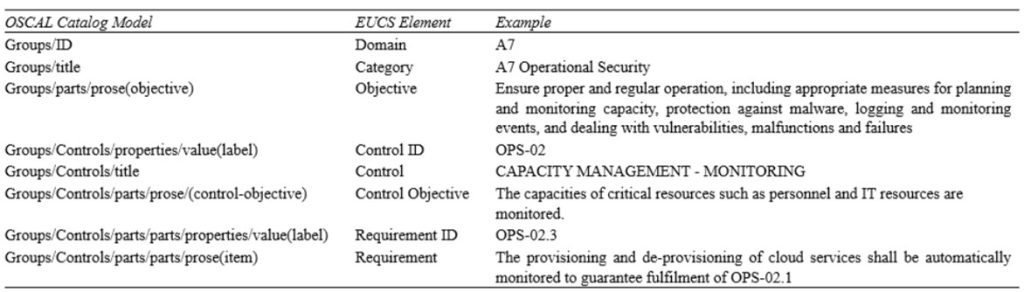
Beyond its own components, EMERALD is actively contributing to the broader European OSCAL ecosystem. In collaboration with the COBALT EU project, an OSCAL-translator module has been produced for the EMERALD framework, extending its applicability further. A generic OSCAL Json template was developed to describe the elements of a scheme, using the Catalog Model (Control Layer) and OSCAL constructs such as groups, controls, parts, properties, and prose.
The EUROSCAL initiative, kicked off by MEDINA, has been advanced by EMERALD to foster a European community around OSCAL adoption for cloud certification. EMERALD has also maintained direct engagement with NIST, the creator of OSCAL, contributing European cloud certification perspectives to the ongoing development of the standard. This dialogue was further deepened in a dedicated meeting with Michela Iorga, the main creator of OSCAL, where the team presented an overview of EMERALD, the RCM Converter module, and the design of the OSCAL schemas, along with a live demonstration of the import/export functionality.
On the European policy side, EMERALD representatives participated in the first meeting of the OSCAL Task Force, supported by ECSO. This task force is dedicated to advancing automated compliance and OSCAL across Europe, with a particular focus on exploring machine-readable representations of national and European regulatory frameworks.
EMERALD also engaged with European research projects such as COBALT and took part in activities of the European Cybersecurity Certification Cluster (EC3), linking the project to broader initiatives on cybersecurity compliance and certification.
Publications and knowledge sharing
EMERALD’s work on OSCAL was also disseminated through research publications and conference presentations, including:
- Beyond Static Audits: Using OSCAL to Streamline Continuous Cybersecurity Certification. This paper addresses the challenge of automating cybersecurity compliance and certification processes for cloud services and presents how OSCAL enables interoperable, machine-readable representations of security controls, implementations, and assessment results.
- Beyond Static Audits: Using OSCAL to Streamline Continuous Cybersecurity Certification – presented at the ETSI Security Conference 2026 in collaboration with the COBALT project.
Leave a Reply